Enabled by default
All services include integrated protection. Customize protection rules through the control panel when needed.
Continuous detection and malicious-traffic filtering,
from the network edge to data centers. Protection already included in your service.
A distributed denial-of-service attack attempts to overload websites, servers and applications with malicious traffic. It can cause slowdowns, downtime and harm your users' experience.
L2JCenter infrastructure detects and filters traffic at different network points before it reaches its destination. All servers and services already include Automatic DDoS Protection, with no additional purchase.
Understand the defense layers ↗ NETWORK · DATA CENTER · SERVICE
All services include integrated protection. Customize protection rules through the control panel when needed.
A distributed network to detect and filter malicious traffic from different sources.
From web hosting to your server infrastructure, protection is included, with mitigation that activates in seconds.
More than 17 Tbit/s of attack-filtering capacity across the global infrastructure.
Active detection to identify malicious traffic and apply filters during an incident.
Defense stays active during attacks, without additional charges for volume or incident count.
Filtering layers combine specialized equipment and systems to protect services of different sizes.
L2JCenter's protection policy keeps your traffic from being shared with third parties.
Adapt protection rules to your IP, service and application's needs.
Advanced firewall rules at the edge help reduce server overload during high-traffic incidents. They can be applied to your IP based on your project's needs.
The infrastructure distributes mitigation across modules to filter network traffic and reduce the impact on latency. VAC combines analysis and filtering technologies that keep evolving.
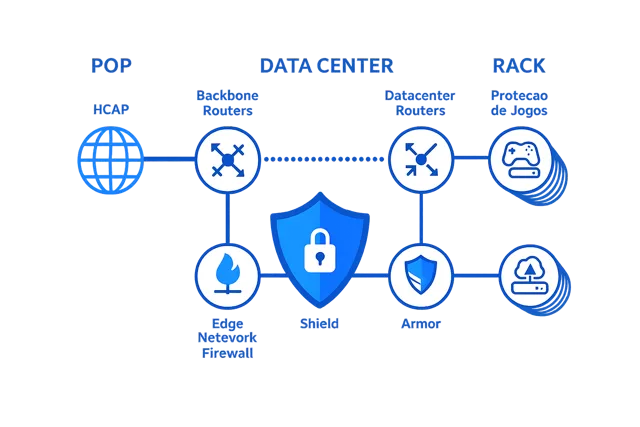
The first network barrier for applying rules and filtering suspicious traffic.
A specialized layer to absorb and neutralize volumetric attacks.
A defense module for more complex attacks, including protocol and application exploits.
Some attacks exploit application logic and require analysis beyond packet volume. Websites and games may need specialized layers to identify that behavior.
Explore L2JCenter's advanced protection solutions and choose the service that fits your project.
VPS, hosting, game servers and dedicated servers include integrated network protection. Choose the service for your project.
The infrastructure is designed for major DDoS vectors, including distributed overload, packet floods, SYN floods, IP spoofing and malformed or amplification attacks.
Network filtering matters because an attack can saturate the uplink before reaching the server. Defense layers work at different points in the infrastructure.
All services include integrated DDoS protection: VPS, dedicated servers, game services and web applications. Traffic passes through detection and mitigation layers before reaching your service.
An attack can consume bandwidth and connection resources, causing slowdowns or downtime. Distributed detection and filtering help separate malicious traffic from legitimate access before it reaches the application.
Yes. Detection stays active continuously. Suspicious behavior triggers mitigation with specific analysis and filters. Once traffic returns to normal, mitigation stops and detection keeps running.
There is no monthly incident limit for L2JCenter DDoS protection. Detection, filtering and mitigation remain available for isolated or repeated attempts, without additional per-attack charges.
Protection is not sold with a traffic allowance that stops mitigation when reached. Malicious traffic keeps being filtered during an attack, without additional volume charges. Global filtering capacity exceeds 17 Tbit/s.
VAC is part of the DDoS infrastructure at data centers used by L2JCenter. It combines traffic analysis and filtering to identify and block attacks. Its layers include Edge Firewall, Shield for volumetric attacks and Armor for more complex attacks.
Yes. Protection rules can be adjusted in the control panel according to your service's features. Read documentation or ask the team for guidance on suitable rules.
Get guidance ↗Choose an L2JCenter service with integrated Automatic DDoS Protection.
Integrated protection · No additional cost · Custom rules